Third-party risk management is no longer a procurement-only activity. It is now a core cybersecurity and governance discipline, especially for organisations that need to work across ISO 27001 and NIS2 without creating two separate supplier processes. The

A European manufacturer already runs an ISO/IEC 27001 information security management system. Then NIS2 enters the picture. The ISO 27001 and NIS2 work begins to split into new spreadsheets, new risk registers, new policies, new supplier questionnaires
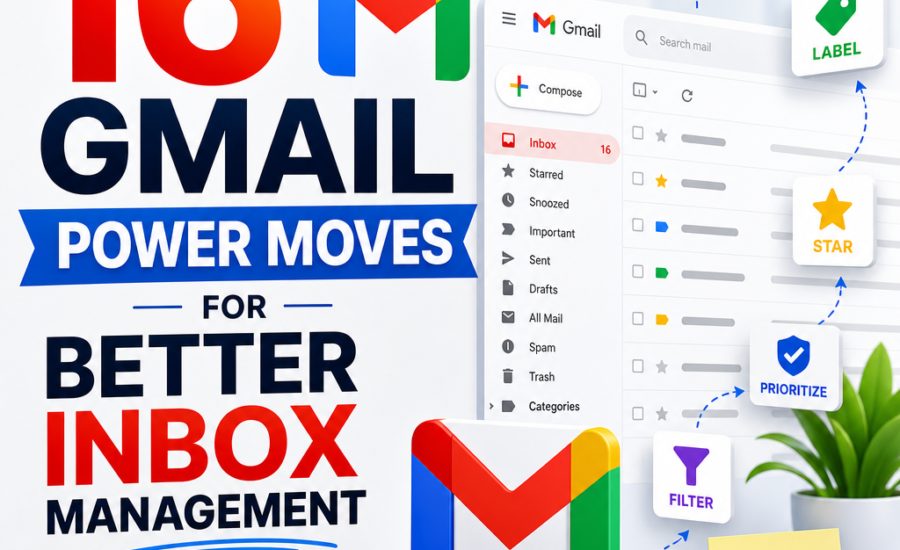
In addition, this guide explains Microsoft 365 Security with practical details and clear takeaways. Email is still one of the most important business tools. However, it also creates daily friction. A cluttered inbox slows replies, buries tasks,
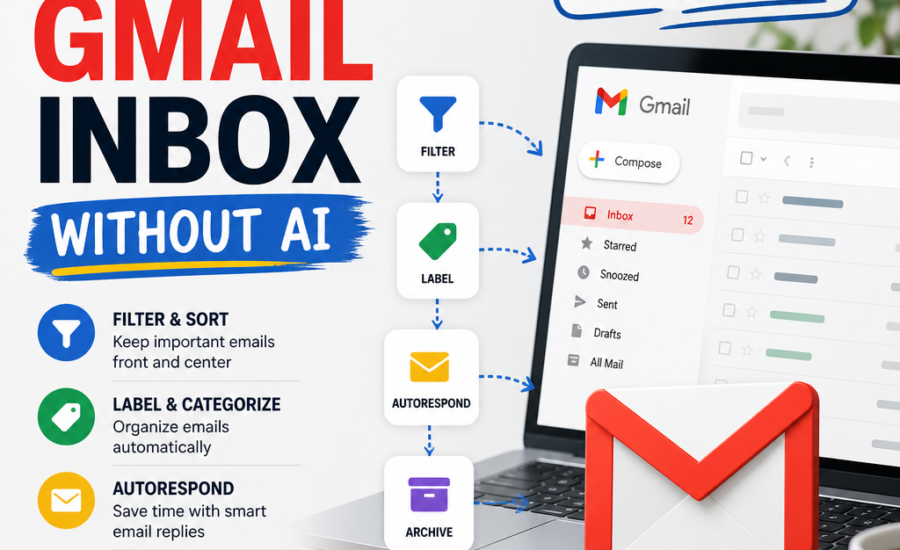
In addition, this guide explains Microsoft 365 Security with practical details and clear takeaways. Email remains one of the most important business tools. However, it is also one of the easiest places for work to become chaotic.
Executive audit readiness is tested the moment a senior manager is asked for the organisation’s current compliance position and cannot answer without gathering spreadsheets, email threads and manually prepared departmental reports. The problem is not a shortage
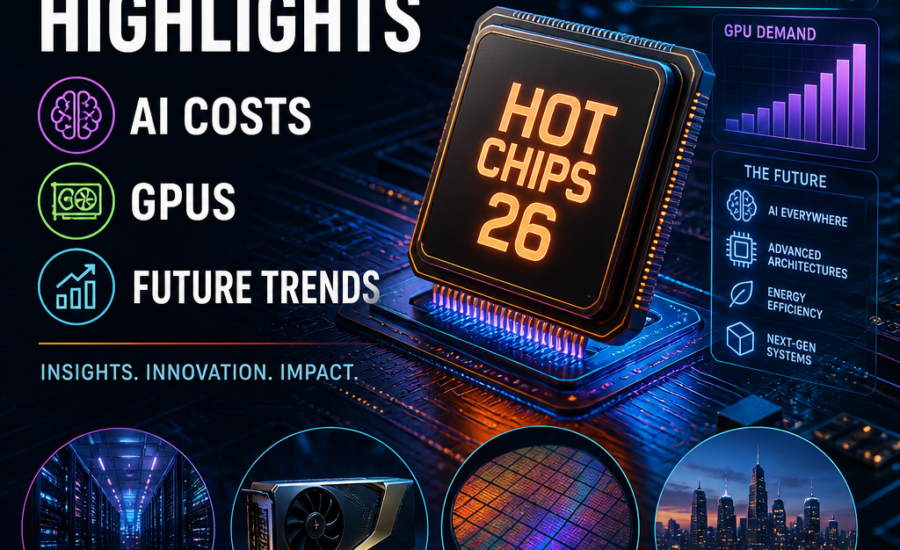
In addition, this guide explains Microsoft 365 Security with practical details and clear takeaways. Hot Chips 26 showed a clear shift in enterprise AI. The focus is moving from raw speed to cost, energy use, and scale.
In addition, the proposed Nvidia and Hugging Face deal could do more than shake up the AI market. It may also change how enterprises choose, deploy, and scale open-source models. For leaders already focused on Microsoft 365
In addition, this guide explains Microsoft 365 Security with practical details and clear takeaways. AI infrastructure is changing quickly, and the assumptions that shaped early enterprise AI strategies are starting to shift. For many organizations, the default
Microsoft Exchange Server Vulnerability and what Microsoft and Security Researchers Have Identified Why the Microsoft Exchange Server vulnerability remains a concern Thousands of Servers Still Need Patching Why This Microsoft Exchange Server Vulnerability Matters for Businesses What
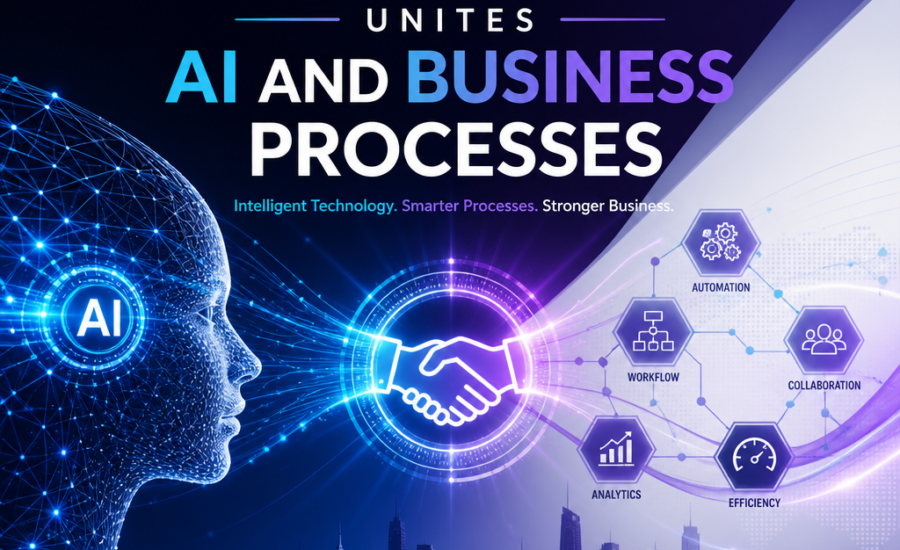
In addition, this guide explains Microsoft 365 Security with practical details and clear takeaways. Artificial intelligence is no longer a standalone initiative. For most organizations, the real opportunity lies in connecting AI with the business processes that
Popular Post


Training and Competence Records: Role-Based Evidence for
November 3, 2026
AI Use Policy for Small Business: Practical
November 2, 2026Instagram Feeds
Popular Posts
IMS Suite Training Records: Practical Evaluation for
November 4, 2026
Training and Competence Records: Role-Based Evidence for
November 3, 2026
AI Use Policy for Small Business: Practical
November 2, 2026Contact Us
Recent Posts
IMS Suite Training Records: Practical Evaluation for
November 4, 2026
Training and Competence Records: Role-Based Evidence for
November 3, 2026
Recent Comments